When your security awareness vendor ships the answer in the headers
Seems like everyone keeps getting these mails, quite annoying and I feel like they arent even that good. I could craft something that most people could click, but that's spearphishing... Would actually be a good test, using AI with some data points on employees to do spearphishing. But I think they are supposed to do this already?
Oh well that's not what we are here for, and this is not a recipe blog.
So the whole thing is pretty simple. KnowBe4 encodes a tracking token in the phishing links so they can report who clicked. But they also send that same token as an X-KB4TOKEN mail header. You can in most email clients use this to filter the messages.
Here you can see that in Outlook:
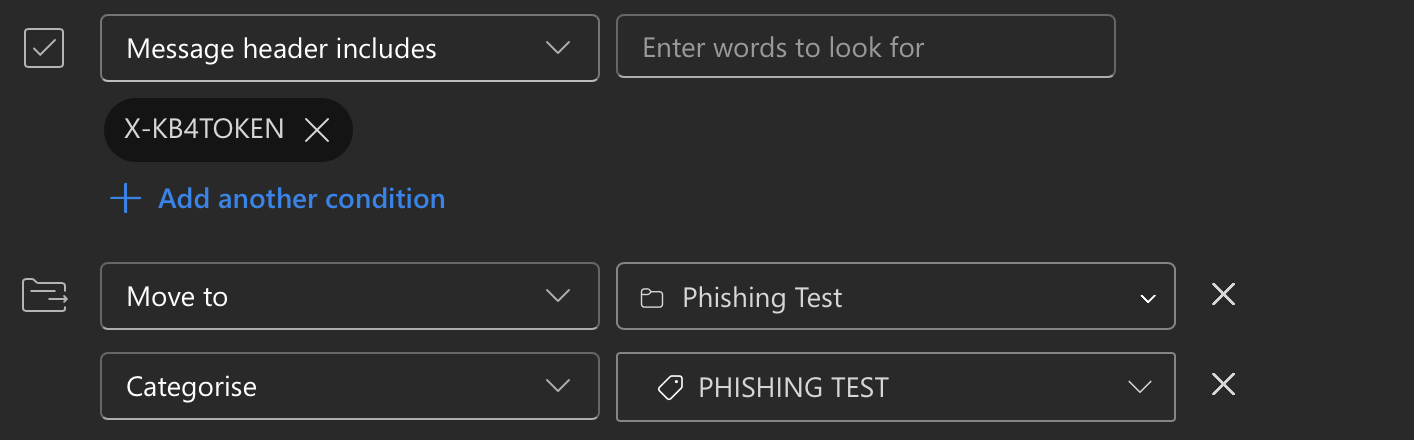
This defeats the purpose of these mails. Now they are all categorized and put in a folder. They could remove this header, but for now it works.
That's all, good categorizing!